Five Years of GitHub Monitoring: Unveiling the Lifecycle of Malicious and For-Sale PoCs
DAY 2
10:40-
11:20
Driven by advances in generative AI, the number of discovered vulnerabilities and of published exploit code and PoCs for verifying them has increased rapidly in recent years. Public repositories such as GitHub are useful platforms for publishing and sharing vulnerability verification code and detection rules for defense, but not every repository or piece of code published there is safe. We have also seen code that does not actually reproduce the target vulnerability, repositories that prompt users to download external files, fake PoCs intended to infect users with malware, and poisoned repositories. Since late 2021, we have continuously monitored vulnerability-related repositories, mainly on GitHub, for about five years, recording publication times, update histories, code similarity, and more. While most of these repositories are published for legitimate purposes, we also found a certain number aimed at malware infection or theft of user information. We have also observed cases that claim to offer PoCs and lead users to sales pages, Proton Mail contact addresses, Telegram, and so on. To investigate these, we created our own hunting rules and analyzed approximately 3,500 repositories from January 1, 2026 to July 1, 2026. The results are summarized below.
- 10 malicious repositories
- Including repositories not yet reported by security vendors or blogs
- Containing references to poisoned Python packages or bundled malware
- 133 suspicious repositories
- Leading users to external communities, listing Proton Mail addresses, etc.
- 122 repositories leading users to PoC sales pages
PoC sales are mediated by e-commerce sites, and because the e-commerce site manages the Bitcoin receiving addresses, tracking the sellers is difficult. We therefore tracked PoCs based on the file hashes listed on the sales pages, and uncovered part of the PoC distribution lifecycle: sale, purchase and publication by a third party, and reposting by other users. In this talk, we will share our analysis results and technical explanations of “techniques used in malicious repositories” and “trends in luring users to malicious repositories and sales pages, and the vulnerabilities they skew toward,” and raise awareness of these threats. We will also release the hunting rules used to discover the malicious and suspicious repositories in this research, along with a list of malicious users identified to date. This will provide clues for investigating PoCs on GitHub and ways to use repositories safely.
-
Location :
-
Track 1(HALL B)
-
-
Category :
-
Technical
-
-
Share :
Speakers
-
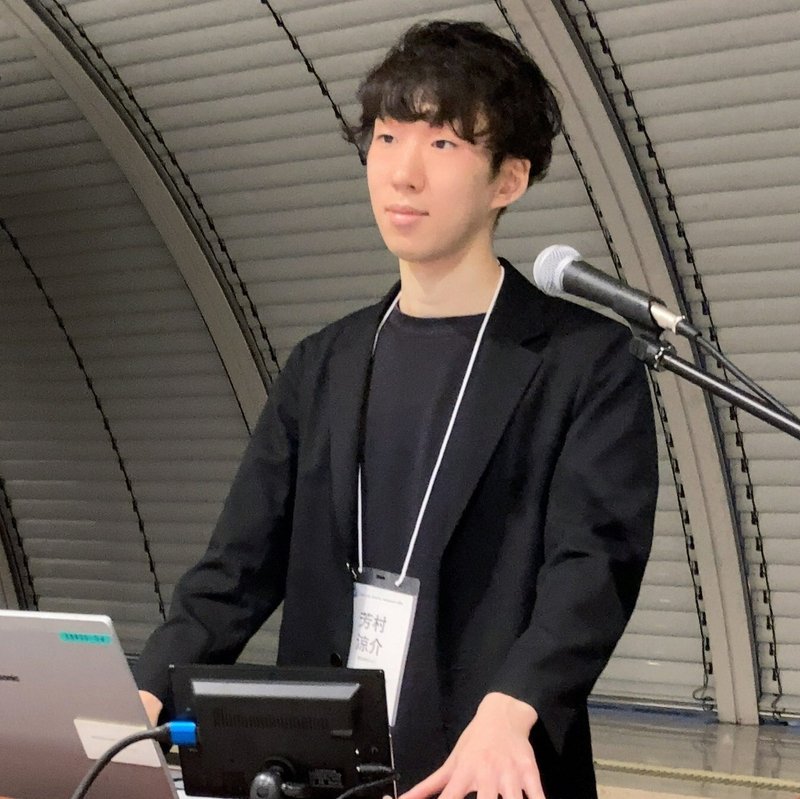
Ryosuke Yoshimura
芳村 涼介
Ryosuke Yoshimura was a bachelor of IT and Information Sciences.
Ryosuke is working in exploitation research, AI development and cyber threat sensory analysis.
He gave lectures and presentation at academic conferences in Japan and JSAC (Japan Security Analyst Conference) and Lightning Talk sessions in FIRST Annual Conference.